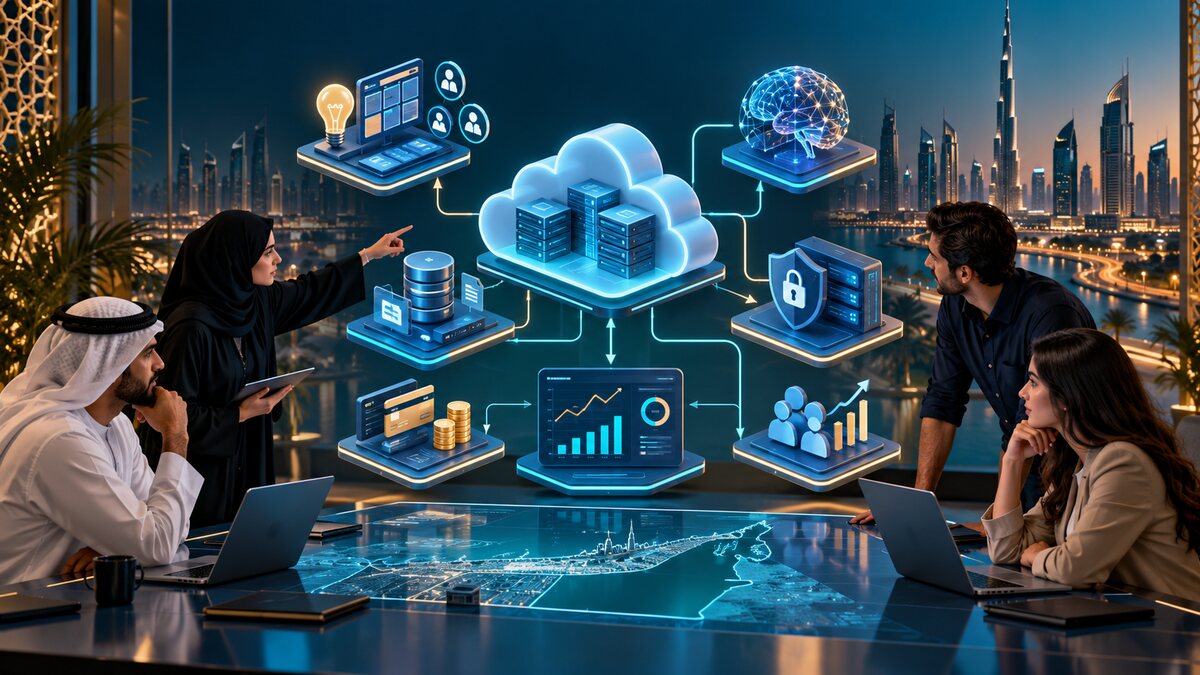
The best AI SaaS development strategies for UAE startups begin with a narrow business problem, not a long feature list. A startup should prove that customers will repeatedly use and pay for one valuable workflow before it builds a large platform around it. AI can improve that workflow, but the product still needs dependable authentication, tenant isolation, billing, monitoring and support.
The UAE's Digital Economy Strategy and AI Charter show a clear national direction toward digital products and responsible AI adoption. That creates opportunity, but it does not remove the normal startup constraints of limited time, budget and engineering capacity. The winning strategy is usually the one that reduces uncertainty fastest while preserving a safe path to production.
When founders compare a software development company dubai, I recommend asking how the team will validate the workflow, control AI cost, protect customer data and recover from failure.
Compare the main AI SaaS development strategies
| Strategy | Best when | Main advantage | Main risk |
|---|---|---|---|
| Workflow-first MVP | Demand is not yet proven | Fast learning with a small scope | Manual work can remain hidden behind the product |
| Managed-service stack | The team needs to launch quickly | Less infrastructure to operate | Vendor limits and rising usage costs |
| Modular monolith | One team owns the product | Simple deployment with clear internal boundaries | Poor discipline can create tightly coupled code |
| Compliance-led architecture | Personal, financial or health data is central | Controls are designed before data spreads | Overengineering before the workflow is validated |
Most early UAE startups benefit from a workflow-first MVP implemented as a modular monolith with managed infrastructure. Stronger isolation or sector-specific controls can then be added where the actual risk requires them.
Start with one measurable customer workflow
Do not begin with a promise to build an AI platform for an entire industry. Choose one user, one repeated problem and one measurable result. A property operations product might classify maintenance requests and prepare a response for staff approval. A finance product might extract invoice fields and flag exceptions without approving a payment.
Write down the trigger, input, decision, output, human approval and success measure. If the workflow cannot be described clearly, AI will not make it clear. During the first pilot, it is acceptable for staff to review every AI result. That review creates the examples and failure cases needed for later automation.
Choose an architecture that a small team can operate
A startup architecture should be easy to understand at 2 a.m. when an important customer reports a problem. For one product team, a well-structured application with clear modules is often safer than many independently deployed services. Frontend, API, background jobs and shared domain rules can remain in one repository while still keeping boundaries between billing, tenants, AI tasks and notifications.
Managed authentication, databases, storage and queues reduce operational work, but each service needs a cost model and recovery plan. Serverless functions suit uneven workloads, while long AI tasks belong in a durable job system.
Teams researching software development dubai should look for practical ownership across the interface, API, data model and deployment. An early SaaS product is damaged when every production issue must cross several disconnected specialists before anyone can trace the complete request.
Design tenant isolation and authorization before growth
Multi-tenant SaaS stores data for several customer organisations in one product. Every request must therefore establish the authenticated user, their tenant and their permission for the requested resource. A tenant identifier submitted by the browser is not proof of access.
AWS describes tenant isolation as a foundational SaaS concern. The application should derive tenant context from a trusted session, apply it in the service and data layers, and test that one organisation cannot read or modify another organisation's records. Database policies such as PostgreSQL Row Level Security can add defence, but they do not replace correct application checks.
The real scope behind Web application development Dubai includes secure server entry points, protected secrets, resource-level authorization, rate limits and production verification. Hiding an admin button in the browser is a usability decision, not a security boundary.
Keep AI behind deterministic product controls
The AI model should suggest, classify, draft or plan. Normal application code should decide what data the model can receive and which actions are allowed. Tool inputs need validation, sensitive actions need approval, and every important result should have a traceable source or audit record.
Use the least expensive model that meets a tested quality threshold. A small model may handle classification while a stronger model processes difficult exceptions. Set maximum input size, output length, tool calls, retries and execution time for each workflow. Without these limits, one unusual document or repeated loop can damage the unit economics of the product.
Maintain a small evaluation set from real, permission-safe examples. Run it when prompts, models or retrieval logic change. OpenAI's production guidance recommends pinned model versions and evaluations for consistent behaviour. A successful demonstration is not evidence that every future input will behave correctly.
Build billing and unit economics into the product model
AI cost is part of the product, not only an infrastructure bill. Estimate the model, storage, search, email, payment and support cost for one active tenant. Then compare that cost with the subscription price and expected usage. A plan that looks profitable at average usage may fail when a small group of customers consumes most of the AI budget.
Meter meaningful activity such as documents processed, AI jobs completed or team seats. Show customers clear limits before they reach them. Use hard limits for abuse protection and soft warnings for normal growth. Store provider usage with an internal job or tenant identifier so a cost spike can be traced to a feature and customer workflow.
Engineer for unreliable networks and partial failure
Production systems fail in pieces. An AI provider can time out after the application creates a job. A payment can succeed before its webhook arrives. A user can lose connectivity while submitting a field report. The product needs explicit states such as queued, processing, awaiting approval, completed and failed.
Background tasks should use idempotency keys and controlled retries. Store enough progress to resume safely, but do not repeat an external action blindly. Give support staff a request identifier, current state and safe retry option instead of forcing them to inspect raw logs.
For field teams and customers with unstable connections, app development Dubai can include a local queue and clear synchronization states. Offline support is not simply caching a page. Conflicts, expired sessions and duplicate writes still need server-side rules.
Apply UAE privacy and security requirements early
The UAE Personal Data Protection Law includes requirements around lawful processing, security measures and data-subject rights where the law applies. A startup should identify which personal data it collects, why it is needed, who receives it, where it is processed and how long it is retained. Sector and free-zone rules may add further obligations.
Collect the minimum data required for the workflow. Redact unnecessary sensitive fields before sending content to an AI provider. Encrypt data in transit and at rest, restrict production access, rotate credentials and avoid placing complete customer prompts in routine logs. Prepare a deletion and export process before a customer requests one.
This article is an engineering guide, not legal advice. Founders should review the official legislation and obtain qualified advice for their organisation, sector and processing activity.
Use a controlled 90-day launch plan
- Days 1 to 15, validate: interview target users, map one workflow, define the success measure and test a manual or clickable prototype.
- Days 16 to 45, build the foundation: implement authentication, tenant context, the core workflow, audit events and the smallest useful AI integration.
- Days 46 to 65, harden: add evaluation cases, cost limits, failure states, backups, monitoring and security tests across tenant boundaries.
- Days 66 to 80, pilot: onboard a small group, review every exception, measure completion time and remove features that do not improve the workflow.
- Days 81 to 90, decide: compare product usage, support effort, AI cost and willingness to pay before expanding automation or architecture.
AI SaaS development strategy FAQ
What is the best technology stack for an AI SaaS startup?
The best stack is one the team can ship, secure and operate. A common starting point is React or Next.js, a Node.js API, PostgreSQL, managed authentication, object storage and a durable queue. The exact tools matter less than clear boundaries, monitoring and tenant-safe data access.
Should a UAE startup build a custom AI model?
Usually not at the MVP stage. Start with a hosted model and collect evidence about quality, latency, privacy and cost. Consider fine-tuning or a custom model only when a repeated, measurable limitation justifies the data and operational investment.
Is a modular monolith suitable for SaaS?
Yes. It can give a small team simple deployment and debugging while preserving clear domain modules. Services can be separated later when scaling, compliance or team ownership creates a real boundary.
How should an AI SaaS product control model costs?
Set per-workflow limits for input, output, tool calls, retries and execution time. Route simple tasks to smaller models, cache safe reusable results, meter usage by tenant and alert when cost per completed workflow changes unexpectedly.
Does every AI action need human approval?
No. Read-only summaries and low-risk drafts may run automatically after testing. Financial, destructive, external-facing or permission-changing actions should normally require stronger verification and often human approval.
When should a startup use microservices?
Use them when independent scaling, regulatory isolation or separate team ownership creates a clear benefit. Do not adopt them only because large technology companies use them. Each service adds deployment, observability and failure-handling work.
How can founders test tenant isolation?
Create users in separate organisations and run negative tests against every sensitive API and database operation. Change resource identifiers, remove memberships and test stale sessions. The correct result is a server-side denial without leaking whether another tenant's record exists.
What should be measured during an AI SaaS pilot?
Measure workflow completion, correction rate, latency, failure rate, human review time, AI cost, support effort and willingness to pay. Usage alone can be misleading if customers repeatedly retry because the result is wrong.
Final takeaway
The strongest AI SaaS strategy for a UAE startup is controlled progress. Validate one valuable workflow, choose an architecture a small team can operate, enforce tenant boundaries, place deterministic controls around AI, understand unit economics and expand only when real usage supports the next investment.
For current context, review the official UAE Digital Economy Strategy, UAE AI Charter, UAE Personal Data Protection Law, AWS SaaS tenant-isolation guidance and OpenAI production API guidance.
If you are planning an AI SaaS product, review my AI SaaS development services or discuss the product architecture with me.
Written from production experience