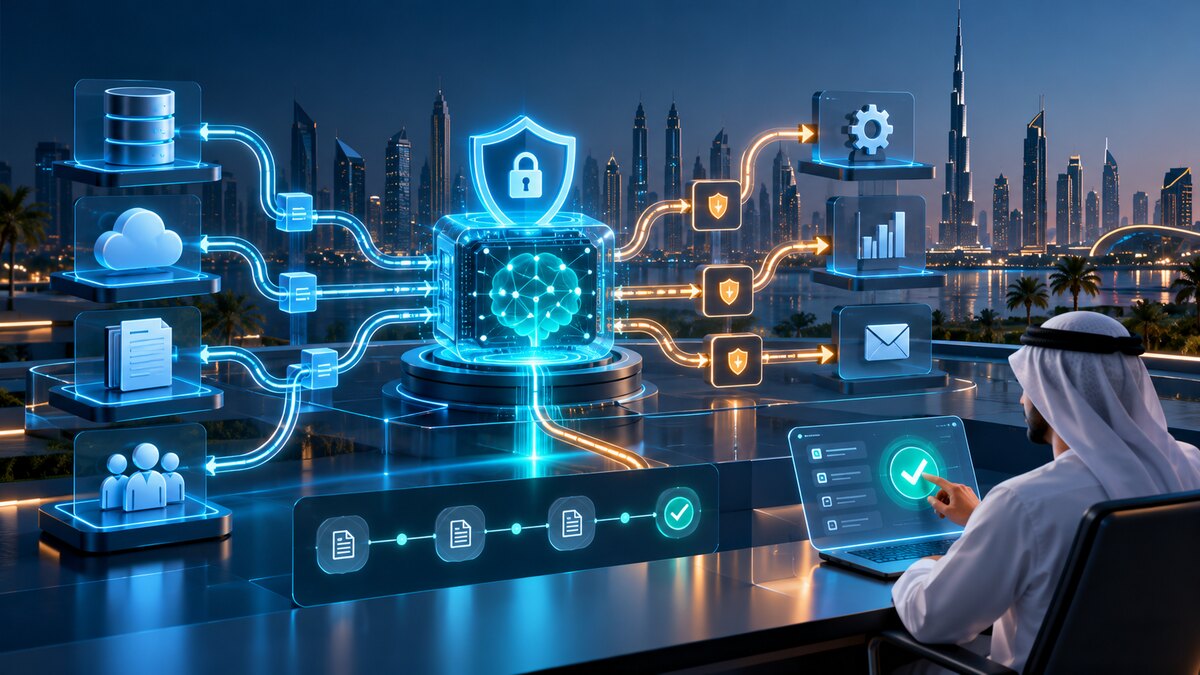
Agentic AI can do more than answer questions. It can choose tools, retrieve business data, update systems and continue working through a task until it reaches a result or needs human help. For UAE businesses, this creates practical opportunities in customer service, operations, finance, sales and internal administration. It also creates a larger security responsibility than a conventional chatbot.
Dubai's private-sector Agentic AI initiative shows how seriously the region is treating this shift. The programme includes specialist training, incubators and support for companies adopting agentic systems. However, adoption should not mean giving an AI model unrestricted access to business systems. A useful agent must operate inside clear technical and operational boundaries.
For UAE teams comparing providers under the search term Web development company Dubai, the important question is not whether a company can connect an AI model to an API. The real question is whether it can build a secure application around that model, with reliable permissions, audit trails, approval steps and failure recovery.
Start with a bounded business workflow
The safest first agent is not a general-purpose digital employee. It is a narrowly scoped system responsible for one measurable workflow.
Consider an accounts-receivable assistant. Its approved job might be to:
- identify overdue invoices;
- retrieve the relevant customer and payment history;
- prepare a follow-up message;
- ask a staff member to approve it; and
- record the approved action in the CRM.
This workflow has a clear starting point, approved data sources, defined tools and a stopping condition. It is easier to test than an open-ended instruction such as "manage overdue accounts."
Before development begins, the business should document the trigger, required inputs, permitted decisions, available tools, actions requiring approval and expected completion result. If every step is already known, a deterministic workflow may be better than an autonomous loop. AI should be introduced only where judgement, interpretation or flexible planning adds real value.
Put application code in control
The language model should propose actions, but normal application code should decide whether those actions are allowed. This separation is the foundation of secure agentic architecture.
For example, the model may request a getCustomerInvoices tool. The server must still authenticate the user, identify the tenant, validate the requested customer ID and limit the returned fields. A system prompt saying "do not access another company" is not access control.
This is where experienced Node.js development becomes important. A Node.js service can sit between the model and business systems, expose a small registry of approved tools, validate every argument and record each tool call. The agent never receives direct database credentials, unrestricted API tokens or permission to execute arbitrary code.
Tools should also be classified by risk:
- Read-only tools may search approved records or retrieve policy information.
- Draft tools may prepare a message, report or recommended change without publishing it.
- Write tools may update a CRM, create a ticket or change a business record.
- High-impact tools may send external communication, approve payments, delete data or alter account access.
The higher the impact, the stronger the approval and verification requirements should be. Financial, destructive and external-facing actions should normally pause for human review.
Protect UAE customer and employee data
An agent may process personal data from emails, support conversations, invoices, HR records or CRM systems. UAE businesses therefore need to examine the workflow against applicable privacy and sector requirements, including the UAE Personal Data Protection Law where it applies.
The application should collect only the fields required for the task. Sensitive information should be redacted before it enters a model when the full value is unnecessary. Logs should avoid storing complete prompts or tool outputs by default, especially when they contain personal, financial or confidential business data.
Teams should document:
- why each category of data is processed;
- which model and infrastructure providers receive it;
- where data is stored and processed;
- how long prompts, outputs and traces are retained;
- how access and deletion requests are handled; and
- whether a legal basis, consent or sector-specific control is required.
The official UAE Personal Data Protection Law should be reviewed with qualified legal or compliance advisers for the organisation's exact circumstances. A technical checklist is useful, but it is not a substitute for legal assessment.
Defend tools from prompt injection
Agentic systems often read untrusted content such as customer emails, uploaded documents, web pages or support tickets. That content can contain instructions designed to manipulate the model. A malicious document may tell the agent to ignore its rules, reveal private data or call a sensitive tool.
Untrusted content should be treated as data, not as authority. The application can reduce risk by extracting limited structured fields, separating instructions from retrieved content and requiring strict schemas for tool arguments. Tool permissions should be enforced using the authenticated user's identity and tenant, not values invented by the model.
OpenAI's current agent safety guidance recommends layered guardrails, tool approvals and evaluations rather than relying on a single prompt. OWASP's Agentic AI threats and mitigations also provides a useful threat-model reference for teams assessing autonomous behaviour and tool misuse.
Engineer for retries, duplicates and partial failure
Business workflow automation must remain reliable when APIs time out or a task restarts. An agent may repeat the same action after a network failure, even when the first request succeeded. Without protection, this can create duplicate tickets, repeated emails or multiple financial operations.
Each write action should use an idempotency key or another deduplication mechanism. The system should persist workflow state outside the model conversation, record completed steps and resume from a known checkpoint. Retries should be limited and safe, while irreversible actions should never be repeated automatically without verification.
The application should also enforce maximum steps, execution time and cost. If an agent cannot finish within those limits, it should stop and escalate to a person instead of continuing indefinitely.
This is why Full stack development matters for an agentic product. The user interface, authentication, backend APIs, database policies, queues, observability and AI layer must work as one controlled system. A capable model cannot compensate for weak tenant isolation or unreliable backend design.
Test the path, not only the final answer
A correct-looking response does not prove that an agent behaved safely. Testing should cover the complete execution path.
Teams should create evaluation scenarios for normal tasks, missing information, malicious input, cross-tenant identifiers, duplicate requests, unavailable tools and ambiguous approval decisions. Reviews should examine which tools were selected, what arguments were sent, whether permissions were enforced and why the run stopped.
Production monitoring should track completion, escalation, latency, cost, repeated tool calls and failed approvals. Audit records need correlation IDs so a team can reconstruct a run without exposing unnecessary sensitive data.
Roll out automation in controlled stages
A secure rollout can begin in observation mode. The agent analyses a task and recommends an action, but cannot change anything. After its recommendations perform reliably, the business can allow it to create drafts. Low-risk, reversible actions may then be automated, while higher-risk actions continue to require approval.
A disciplined custom application development process should include threat modelling, privacy review, evaluation datasets, pilot users and a rollback plan before wider deployment. The team should expand autonomy based on evidence from real runs, not because a demonstration appeared convincing.
Secure agentic AI FAQ
What is the safest first agentic AI workflow for a UAE business?
Start with one bounded, low-risk workflow with clear inputs, approved tools and a measurable result. Drafting a reply is safer than changing records automatically.
Does every agent action require human approval?
Approval should match the risk. Read-only searches and drafts may run after testing. Customer communication, payments, record changes and access changes should require a person.
How should an AI agent protect UAE customer data?
Collect only required data, redact sensitive fields, enforce tenant isolation, define retention, review providers and obtain advice about applicable UAE privacy requirements.
How can prompt injection be stopped from triggering business tools?
Treat external content as untrusted data. Authenticate users, validate arguments, enforce tool allowlists, require approval for sensitive actions and test cross-tenant attacks.
What should be tested before an agentic AI production launch?
Test normal tasks, missing data, denied approvals, malicious input, duplicates and outages. Verify limits, audit logs, safe retries, rollback and human escalation.
Final takeaway
UAE businesses can gain real value from agentic AI in 2026, but safe automation requires more than connecting a model to company software. The strongest systems use bounded workflows, server-enforced permissions, carefully scoped tools, human approval, privacy controls, durable state and detailed evaluations.
Start with one workflow where success can be measured. Keep the application in control, treat all external content as untrusted and give the agent only the access required for that task. Once the system proves reliable under real operating conditions, its responsibilities can grow without turning business automation into an uncontrolled security risk.
Research references:
Written from production experience