OpenAI announced the Agents API in public beta on September 10, 2026. For SaaS teams, the important change is not another chat endpoint. It is a managed way to run longer agent workflows with tools, isolated environments and multiple specialised agents. That can remove a large amount of orchestration work, but it does not remove the product engineering around permissions, tenant isolation, approvals, testing and cost control.
This OpenAI Agents API guide explains how I would evaluate the new platform for a production SaaS product. I am focusing on the parts that decide whether an agent remains a useful demo or becomes a reliable feature: the system boundary, tool design, human approval, observability and a controlled rollout. The API is new and still in beta, so exact interfaces may change. The architecture principles should not.
What the OpenAI Agents API changes for SaaS teams
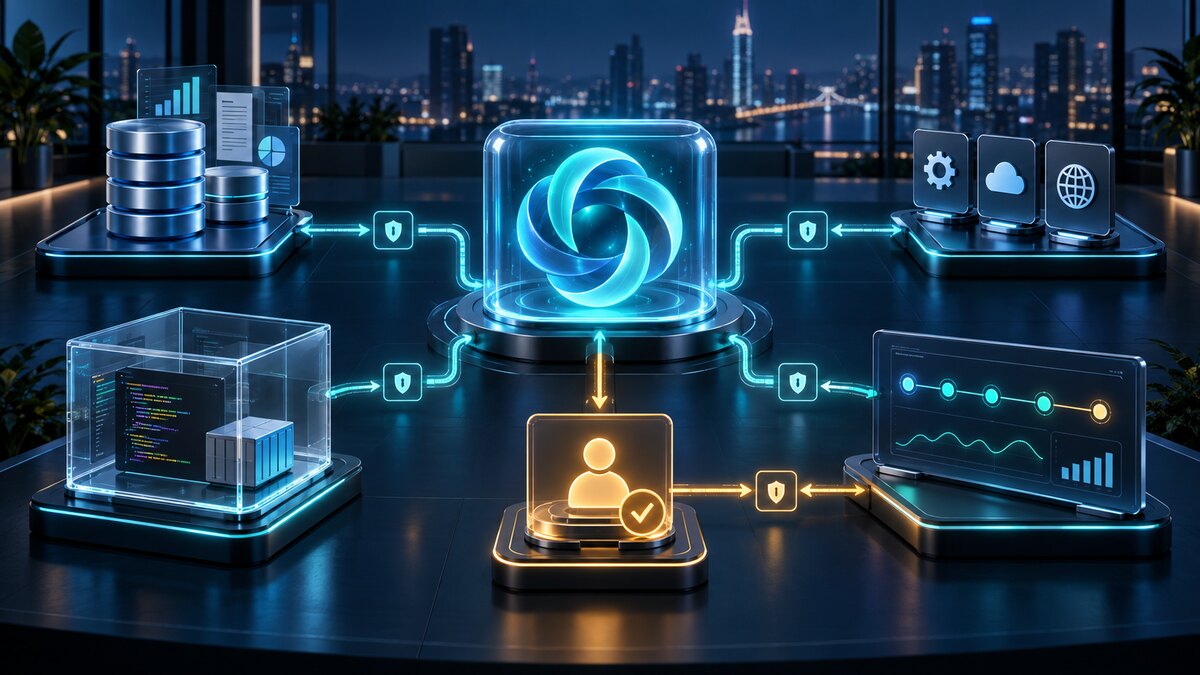
The official Agents API documentation describes a managed harness that can run an agent in an OpenAI-hosted sandbox, on your own infrastructure or through a supported sandbox provider. A session can combine a model, tools, an environment and subagents instead of forcing every product team to assemble the entire loop themselves.
This matters because a useful business agent normally performs more than one model call. It may inspect a request, retrieve account data, call an internal API, prepare a file, ask for approval and then continue. The surrounding system must keep state, deal with failed tools, preserve context and expose enough evidence to understand what happened.
OpenAI is offering more of that execution layer as a managed service. I see the main benefit as faster delivery of well-bounded workflows, not permission to give a model unrestricted access to a business. The API can coordinate work, but your application must still decide which customer owns the request, which records may be read and which actions need confirmation.
A practical OpenAI Agents API production architecture
I would keep the agent behind the existing SaaS backend rather than letting a browser call powerful tools directly. The user signs into the product normally. The backend resolves the organisation, role and subscription, then creates or resumes an agent session with only the context required for that task.
The agent should receive small, purpose-built tools such as getInvoiceSummary, searchApprovedDocuments or prepareSupportReply. It should not receive a generic database connection or a broad internal administrator token. A narrow tool is easier to authorise, test, trace and revoke.
For a multi-tenant product such as an employee engagement platform, tenant identity must come from the authenticated server session. It should never come only from text written by the user or generated by the model. Every data tool should apply the organisation identifier again at the database or API boundary. That is the same defence-in-depth rule I use for ordinary SaaS features: the interface can guide behaviour, but the data layer enforces it.
An isolated sandbox is useful for code execution, file conversion or analysis that should not run inside the main application process. Isolation is not a replacement for limits. The session still needs restrictions on network destinations, available files, execution time, output size and retained data.
Separate the agent from irreversible actions
Read operations, draft creation and final actions should be different tools. An agent may safely search documentation and prepare a response automatically. Sending that response to a customer, issuing a refund or changing an account should pass through a stronger policy and often a human approval step.
type Risk = "read" | "draft" | "write" | "financial";

const toolRisk: Record<string, Risk> = {
  searchKnowledge: "read",
  prepareReply: "draft",
  sendReply: "write",
  issueRefund: "financial",
};

export function needsApproval(toolName: string) {
  return ["write", "financial"].includes(toolRisk[toolName]);
}
This simple separation is more useful than a single vague instruction telling the model to be careful. The server owns the policy, and the agent cannot talk its way around it.
Tool permissions and human approval are product features
The Agents SDK human-in-the-loop flow can pause a run, surface the pending action and resume after approval. In a real SaaS interface, that approval screen should show the action in plain language: what will change, which customer or record is affected, what data will be sent and whether the action can be reversed.
I would define approval rules by risk rather than asking users to approve every tool call. Constant prompts train people to click without reading. Low-risk retrieval can run automatically when normal authorisation succeeds. External messages, destructive changes, financial operations and transfers of sensitive data deserve explicit review.
Guardrails provide another layer. OpenAI's current guardrail documentation distinguishes checks around user input, final output and individual function tools. Tool-level checks are especially important when a workflow contains several agents or handoffs, because the risk lives at the action boundary.
Prompt injection must also be treated as untrusted input, not solved with a stronger system prompt alone. A document retrieved from a knowledge base, a web page or a support ticket may contain instructions aimed at the agent. Retrieved content should provide facts, while server policy decides permissions. Sensitive tools should validate structured arguments and independently load the authorised record instead of accepting a raw URL, SQL query or account identifier from model output.
Tracing, testing and cost control before launch
A production agent needs an answer to a basic support question: what exactly did it do? The Agents SDK tracing system can record model generations, tool calls, handoffs, guardrails and custom events. I would add application metadata such as workflow name, internal request ID, tenant-safe correlation ID, duration, token usage and final status.
Tracing should not become a second uncontrolled copy of customer data. Review what is included, redact secrets and personal information, and align retention with the product's privacy requirements. OpenAI documents options for excluding sensitive trace inputs and outputs, but the application still owns its logging policy.
Testing should cover the workflow, not only the final sentence. The official SDK includes deterministic test doubles for agent and tool behaviour. Useful tests include an unavailable API, a duplicated action, a malformed tool argument, an approval rejection, a tenant mismatch and a session that reaches its turn or time limit.
Cost needs the same visibility as latency and errors. Record tokens, tool calls, sandbox duration and retries by workflow. Set a maximum number of turns and a per-request budget. Use a smaller or faster model for routing and simple extraction when it is reliable enough, while reserving more capable models for decisions that actually need them. A workflow that saves five minutes but unpredictably spends more with every retry is not ready to scale.
A controlled rollout plan for an agent feature
I would launch one narrow workflow first. Good candidates have a clear input, a measurable result and limited consequences: preparing a support reply, summarising an account for an operator, classifying an inbound request or building a draft report from approved sources.
- Define the outcome. Write down what success means, what the agent may access and which actions are forbidden.
- Build narrow tools. Give every tool a strict schema, server-side authorisation and predictable error response.
- Create an evaluation set. Include normal requests, ambiguous instructions, hostile retrieved content and cross-tenant attempts.
- Run in observation mode. Let the agent prepare results without performing external actions, then compare its work with the existing process.
- Add approvals. Enable selected write actions only after the approval interface and audit record are working.
- Release gradually. Start with internal users or a small customer group and monitor completion rate, corrections, latency and cost.
- Keep a fallback. Users need a clear route to manual handling when the agent is uncertain or a dependency fails.
This approach is intentionally less dramatic than promising a fully autonomous employee. It creates evidence quickly and limits the cost of mistakes. Once the workflow is stable, more tools or specialised agents can be added without weakening the original boundary.
When the Agents API is the right choice
The Agents API is a strong candidate when the job genuinely requires multiple steps, tools, persistent state, isolated execution or specialist delegation. A normal API call is still the better choice for simple extraction, classification, summarisation or a single retrieval-and-answer flow. Adding an agent loop where deterministic code already works increases latency, cost and failure modes.
I would also compare the managed execution options with the product's data and infrastructure requirements. Some teams will value the speed of a hosted environment. Others will need their own network boundary or tighter control over storage and logs. The new API explicitly supports different environment choices, so that decision should come from the workload rather than fashion.
For a new SaaS product, the fastest responsible path is usually hybrid: deterministic application code for identity, billing, permissions and final writes; an agent for reasoning across approved tools; and a person for genuinely high-impact decisions.
Practical takeaway
The OpenAI Agents API can shorten the distance between an agent prototype and a production workflow, especially when the product needs long-running sessions, tools, sandboxes or subagents. It does not make the surrounding SaaS architecture optional.
Keep authentication and tenant isolation in the application. Give the agent narrow tools instead of broad credentials. Separate reading, drafting and irreversible actions. Require meaningful approval where risk is real. Trace the complete workflow, test failure paths and set explicit limits on turns, time and cost.
That foundation is what turns an impressive demonstration into software a business can operate and trust. If you are evaluating an AI agent for a SaaS product in the UAE or remotely, I can help define the workflow, architecture and production safeguards before the first integration becomes difficult to unwind.
Written from production experience